Unified Audit Trail, Service Log, and Operator Console Architecture
Resolving Verdict Snapshot v3 Pointers
When an operator opens a governed transaction in the CaberUserConsole, the Express Backend For Frontend (BFF) joins the OpenSearch event metadata (csi_agg_events / csi_audit_unified) with the content addressed Verdict Snapshot v3 blob in GSS.
- Pointer Extraction: The console reads
audit.edge_verdict_snapshot_state,audit.edge_verdict_snapshot_ref(for single chunk snapshots), oraudit.edge_verdict_snapshot_chunksplusaudit.edge_verdict_snapshot_sha256(for multi chunk snapshots) from the OpenSearch event document. - Cryptographic Verification: After streaming the snapshot from GSS via
caber_storage, the BFF verifies that the payload digest matchesaudit.edge_verdict_snapshot_sha256. - Source Coordinate Overlay: The console renders the
redaction_decisionsarray from the v3 snapshot directly over the source payload. Because everyRedactionDecisionanchors itssource_spans(SourceSpan { start, end }) tocoordinate_space: "source", the UI can simultaneously highlight:- Enforced Redactions (
mode: "enforced"): Byte spans that were replaced on the wire, displaying the winningpolicy,driver_nmers, replacement string, and identity minimizedreason. - Simulated Observe Decisions (
mode: "would_have"): Byte spans from policies or hosts running inobservemode (redactEnabled = falseorredactStrategy: "disabled"), allowing compliance teams to preview exact blast radius before switching a policy toenforce.
- Enforced Redactions (
3. Operator Console (CaberUserConsole v3.2.0) Workspaces
3.1 Console Route Map and Functional Proof Surfaces
The compiled operator guide (release-docs-generator) maps each CaberUserConsole route to a concrete functional verification surface:
| Console Route | Workspace View | Functional Proof & Telemetry Surface |
|---|---|---|
/admin/home | Executive Governance Overview | Displays fleet wide governed request volume, active enforce vs observe policy posture, redaction counts, and top contributing CORI sources. |
/admin/audit | Audit V2 Four Zone Workspace | Four zone inspection layout: (Zone 1) Time & Verdict Filter Bar, (Zone 2) Paginated Event Stream (csi_agg_events), (Zone 3) Action Trace Waterfall (trace.trace_id), and (Zone 4) Inline Payload & Verdict Snapshot v3 Diff Inspector. |
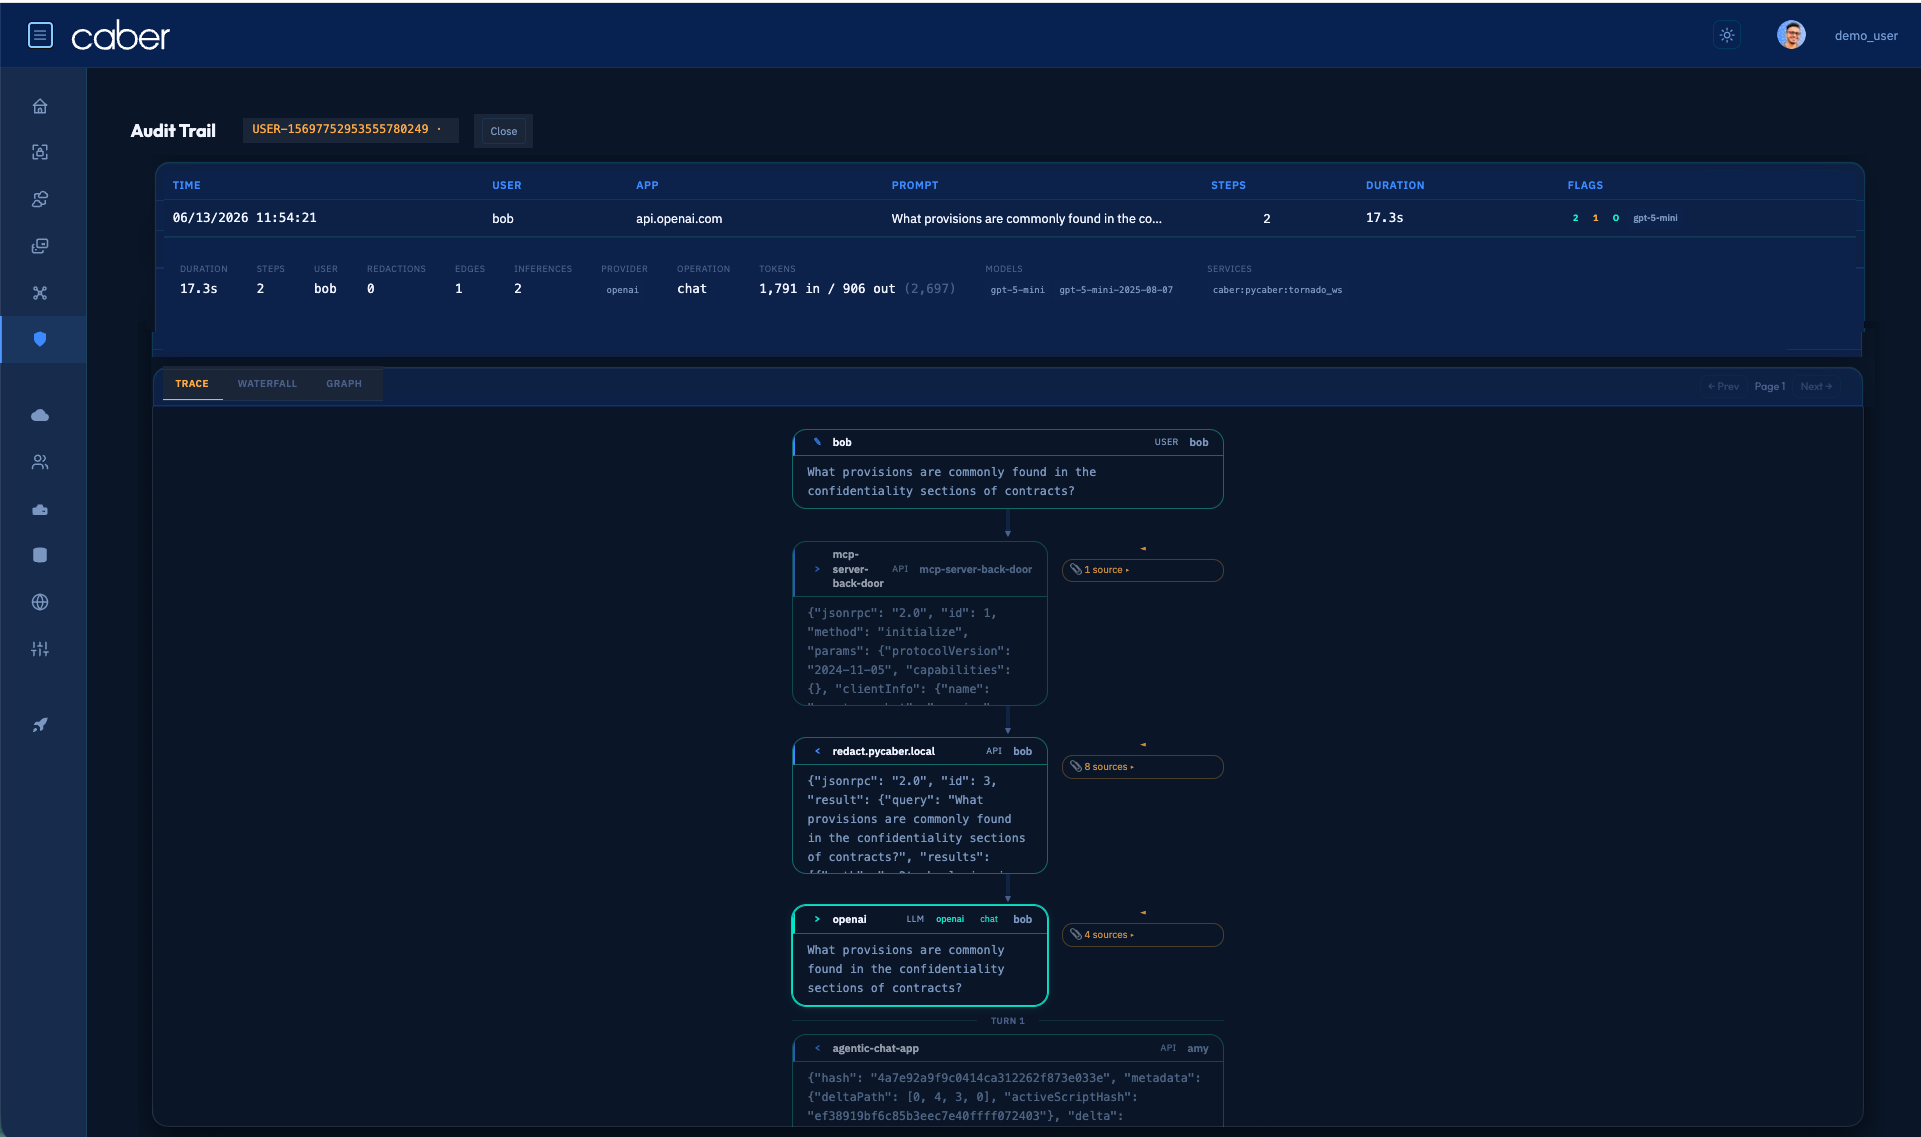
/admin/audit/trail-popup | Trace Detail & Step Inspector Modal | Deep dive per hop modal proving on-behalf-of (obo.user) attribution (100% top 1 principal attribution accuracy and 97.9% surgical redaction detection in CaberEvalBenchmarks), showing exact source_spans redacted vs preserved on each LLM and tool call. |
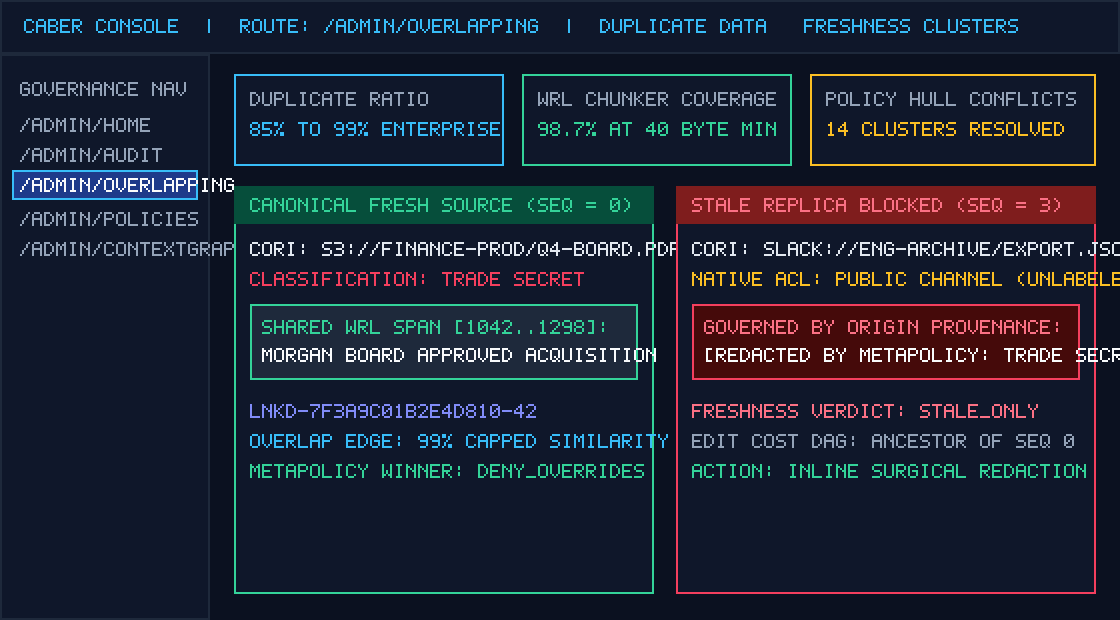
/admin/overlapping | Duplicate Data Tracker & Side by Side Diff | Visualizes cross repository duplicate clusters, 99% capped overlap edges between documents, convex policy hulls (enforce vs observe conflict zones), and side by side chunk comparison between fresh canonical documents (version_sequence == 0) and stale replicas. |
/admin/accessAuth | Principal & Credential Authorization Matrix | Displays resolved iss_sub principals, SCIM directory groups (csi_identity_map), caber.email four step fallback hits, and masked cred_hmac keys. |
/admin/dataFlow | Data Lineage Sankey Diagram | Interactive Sankey flow mapping byte volume and chunk propagation from origin CORI storage buckets through RAG retrievers, MCP servers, and outbound API hosts. |
/admin/discovery | Closed API & Shadow AI Inventory | Live catalog of ApiMapMinter discoveries across the five closed resource types (http-api, mcp, object-store, bash, script) with first called and last called timestamps. |
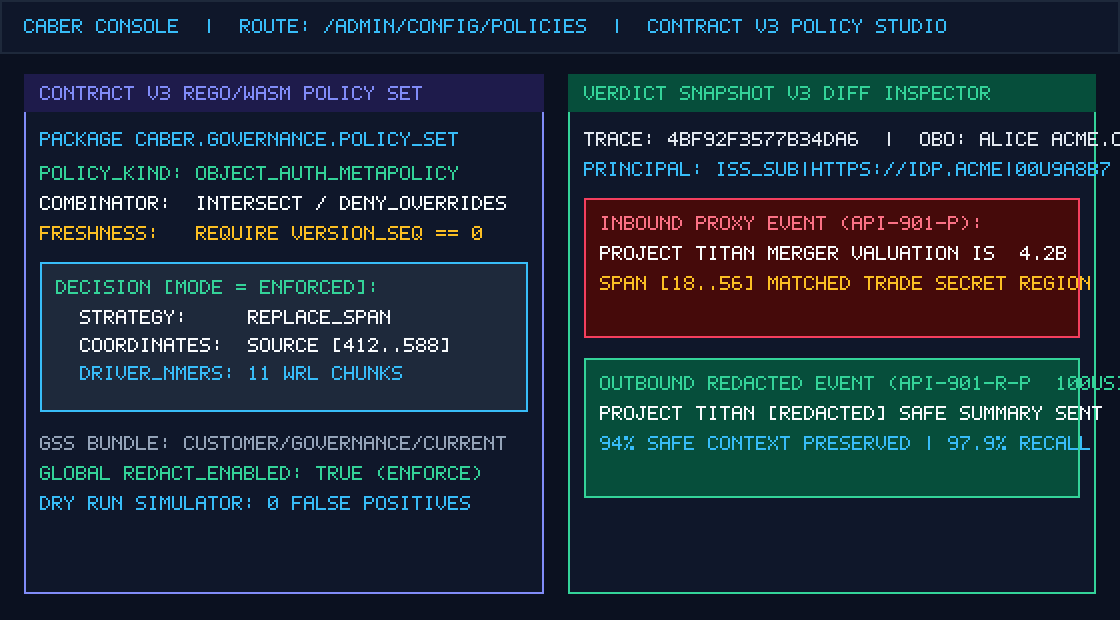
/admin/config/policies | Contract v3 Policy Studio | Authoring, priority ordering, and observe_all dry run simulation for system, framework, data_use, and object_auth_metapolicy Rego bundles, contrasted against coarse over blocking (100% document deny) and regex under blocking failure modes. |
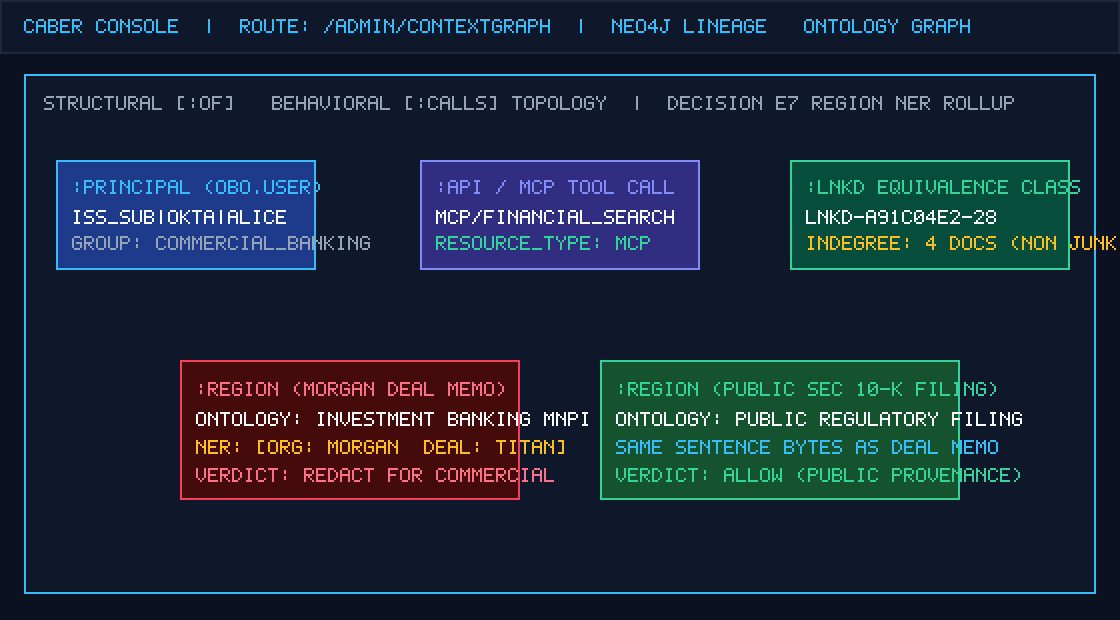
/admin/contextGraph | Interactive Neo4j Context Graph Explorer | Force directed neighborhood explorer for :Data, :Region, :Sentence, :LNKD, :Principal, and :API nodes, highlighting LNKD-{xor}-{count} equivalence classes and "Junk" boilerplate hubs. |
/admin/audit/trail-popupAudit V2 Trace Detail & On-Behalf-Of Provenance InspectorAssertion Verified: Proves that Caber binds every multi-hop agent, MCP tool call, and LLM completion to the initiating human principal (100% top-1 OBO attribution accuracy) and records surgical byte-span redactions (97.9% recall) in Verdict Snapshot v3.
/admin/overlappingDuplicate Data Tracker & Side-by-Side Freshness Cluster InspectorAssertion Verified: Proves that Caber detects 85% to 99% enterprise content duplication down to 40-byte WRL sub-sentence phrases (97% to 98.7% coverage), separates canonical fresh sources (version_sequence == 0) from stale replicas, and enforces origin trade-secret policies even when text is copied into unlabeled channels.
/admin/config/policiesContract v3 Policy Studio & Verdict Snapshot v3 Diff InspectorAssertion Verified: Proves that Contract v3 Rego/Wasm policies and multisource metapolicies surgically redact only the unauthorized byte spans ([start, end) in source coordinate space) while preserving 94% of safe surrounding context in the response.
/admin/contextGraphNeo4j Context Graph & Ontological Provenance ExplorerAssertion Verified: Proves that identical sentence bytes in two different documents carry distinct meaning and governance verdicts depending on their ontological neighborhood (:Region NER rollup, LNKD-{xor}-{count} equivalence class, and CORI provenance).
4. OpenSearch Audit and Service Log Query Reference
Querying Enforced and Observed Redactions (csi_agg_events)
GET /csi_agg_events/_search
{
  "size": 25,
  "sort": [{ "event.time": { "order": "desc" } }],
  "query": {
    "bool": {
      "must": [
        { "terms": { "audit.governance_verdict": ["deny", "transform", "clarify"] } }
      ],
      "filter": [
        { "range": { "event.time": { "gte": "now-24h" } } }
      ]
    }
  },
  "_source": [
    "event.id",
    "event.time",
    "trace.trace_id",
    "user.name",
    "user.iss",
    "user.sub",
    "api.host.name",
    "api.path",
    "api.resource_type",
    "audit.was_redacted",
    "audit.governance_verdict",
    "audit.edge_verdict_snapshot_state",
    "audit.edge_verdict_snapshot_ref"
  ]
}
Querying Operator Service Log Errors and Recoveries (csi_service_log)
GET /csi_service_log/_search
{
  "size": 50,
  "sort": [{ "timestamp": { "order": "desc" } }],
  "query": {
    "bool": {
      "should": [
        { "terms": { "category": ["error", "alert"] } },
        { "wildcard": { "event": "*_recovered" } }
      ],
      "minimum_should_match": 1
    }
  }
}