Governance Console & Unified Audit
Every subdocument characterization match, freshness cluster assignment, metapolicy decision, and cross chain principal trace converges into CaberUserConsole v3.2.0. The console provides security engineers, compliance officers, and platform operators with a single control plane for visual policy authoring, live telemetry inspection, provenance graph exploration, and system health diagnostics.
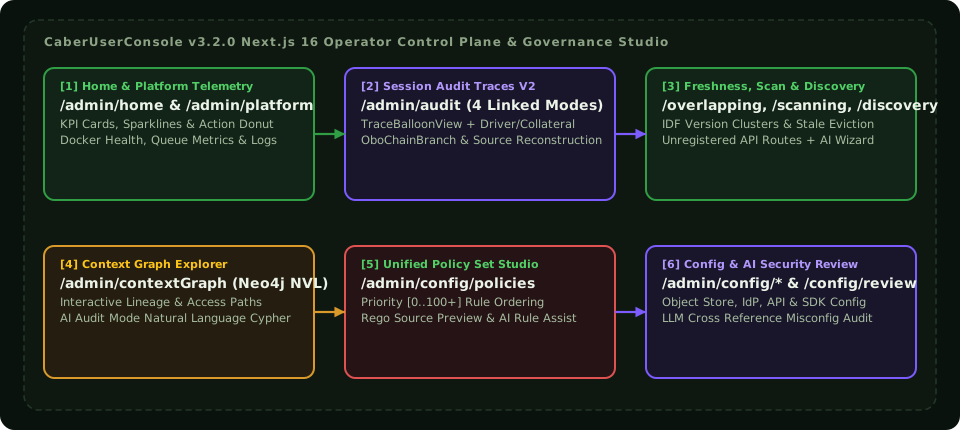
While caber_core and pycaber(auto) operate in band inside application processes and gateways, human operators need an out of band command center to:
- Inspect Unified Audit Trails: Correlate LLM prompts, tool executions, WRL Chunker fragment hits, Principal delegation chains, and metapolicy verdicts in one timeline.
- Author Policies and Metapolicies: Build, test, and publish Rego source policies and multisource metapolicies without editing raw files on disk.
- Explore Data Lineage & Freshness Clusters: Visualize Neo4j document similarity clusters (
CANONICALvsSTALE_REPLICA) and AI output provenance origin trees. - Configure Connectors & Pipeline Parameters: Manage
Identity_Sources,Object_Sources,Metadata_Sources, and runtime configuration snippets viaENV_Manager.
Functional Capabilities by Console Workspace
1. Executive Dashboard & Risk Telemetry (/ and /dashboard)
- Displays live throughput metrics: total characterized tokens per second, WRL Chunker match rate, policy enforcement verdicts (
ALLOW,WARN,DENY,REDACTED), and active stale source interceptions. - Renders time series charts of policy violations broken down by department, Principal role, LLM provider, and data classification tier.
2. Unified Audit & Interaction Inspector (/unified-audit and /interactions)
- Side by Side Payload Diff Viewer: Shows the raw LLM prompt or completion alongside the post enforcement redacted payload, highlighting exact 40 byte WRL Chunker match spans color coded by source document classification (
PUBLIC,internal,confidential,RESTRICTED). - Principal & Agent Chain Waterfall: Displays the W3C trace waterfall (
gen_ai.chat,gen_ai.execute_tool,mcp.tool.call,http.client.request,process.command) annotated with the initiatingPrincipalContextand every intermediate agent incaber.agent.chain. - Decision Receipt Breakdown: Expands any
DENYorWARNevent to show the individual Phase 1SourceVerdictentries, Phase 2 suppressed stale replicas, and the Phase 3 metapolicy combinator calculation.
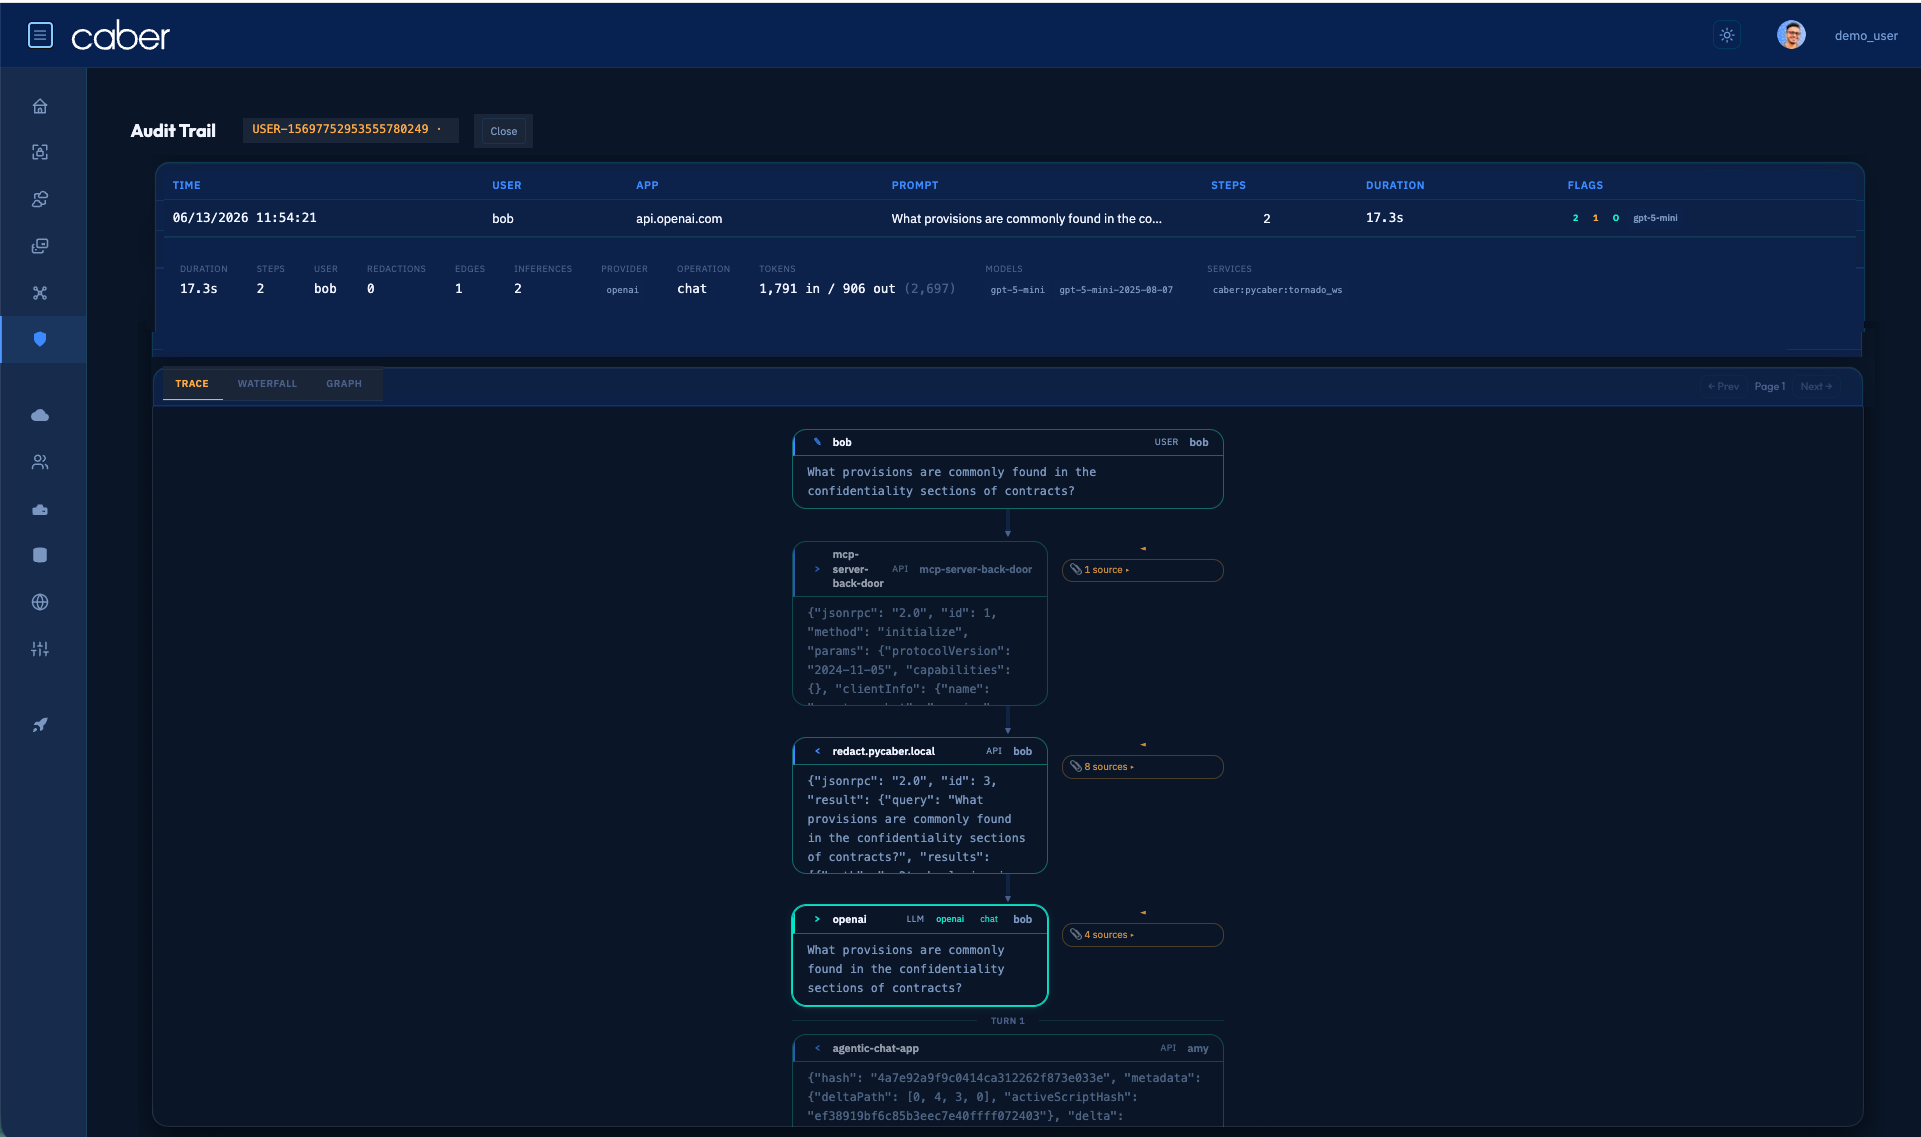
/admin/audit/trail-popupAudit V2 Trace Detail & On-Behalf-Of Provenance InspectorAssertion Verified: Proves that Caber binds every multi-hop agent, MCP tool call, and LLM completion to the initiating human principal (100% top-1 OBO attribution accuracy) and records surgical byte-span redactions (97.9% recall) in Verdict Snapshot v3.
3. Data Lineage, Corpus Explorer & Stale Cluster Graph (/data-lineage and /documents)
- Interactive Cytoscape / force directed graph view backed by Neo4j (
csi-neo4j). - Allows operators to click any enterprise document (
Documentnode) to inspect:- Its current WRL Chunker chunk count and RBIX index residency status.
- Its similarity cluster membership (
SIMILAR_TOandCANONICAL_VERSION_OFedges) showing which stale replicas in S3, Google Drive, or SharePoint are currently suppressed byfreshness_filtered_override. - Every downstream AI completion and tool call (
DERIVED_FROM_FRAGMENT) that has ever used a fragment of that document.
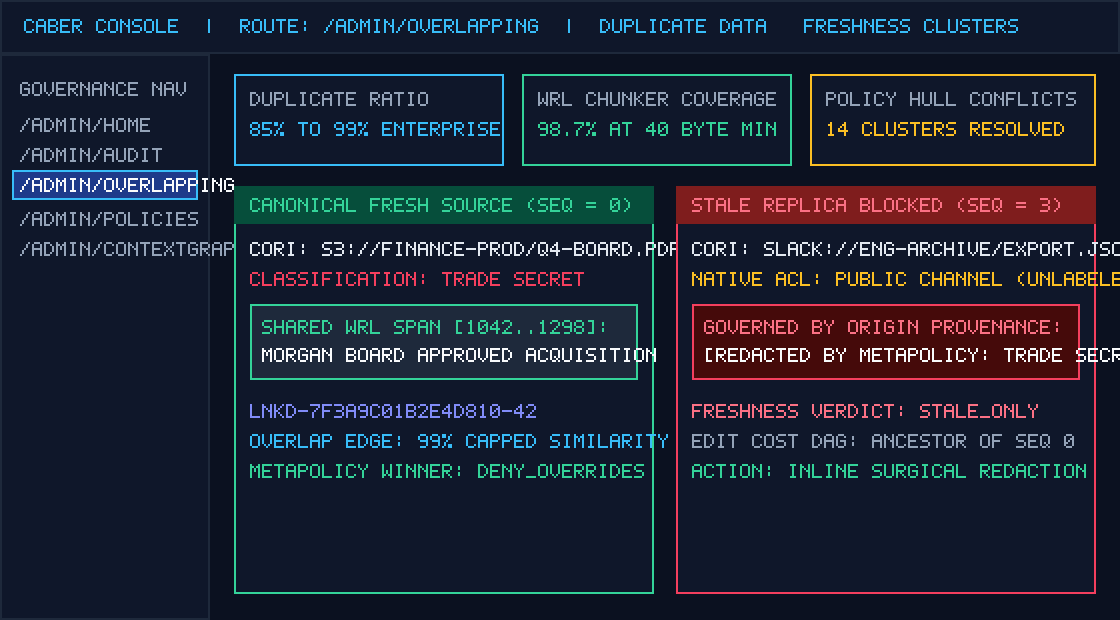
/admin/overlappingDuplicate Data Tracker & Side-by-Side Freshness Cluster InspectorAssertion Verified: Proves that Caber detects 85% to 99% enterprise content duplication down to 40-byte WRL sub-sentence phrases (97% to 98.7% coverage), separates canonical fresh sources (version_sequence == 0) from stale replicas, and enforces origin trade-secret policies even when text is copied into unlabeled channels.
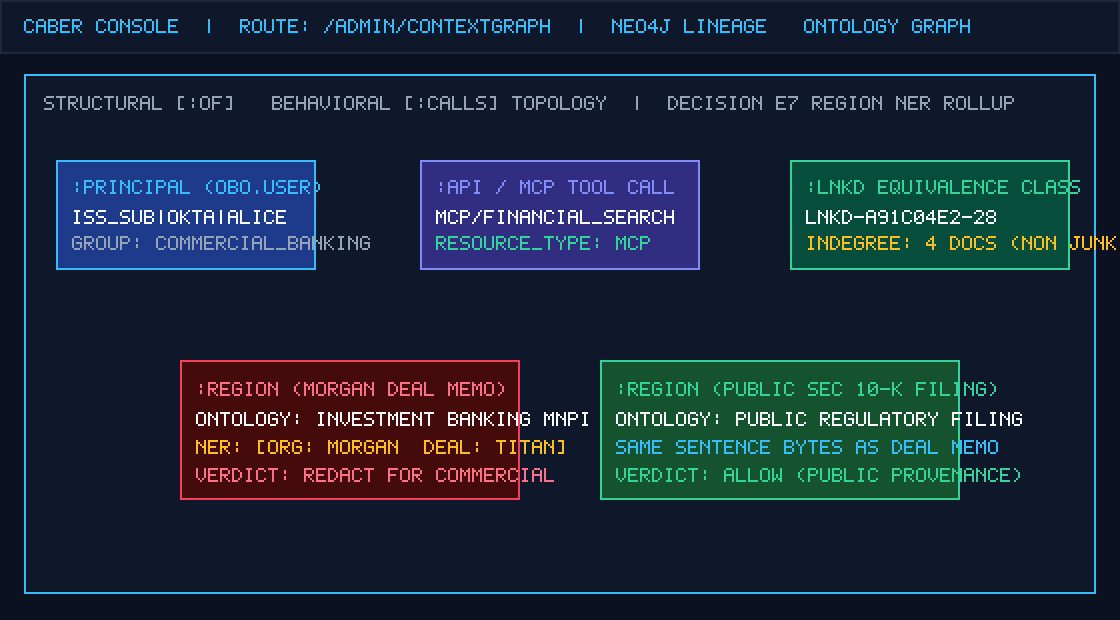
/admin/contextGraphNeo4j Context Graph & Ontological Provenance ExplorerAssertion Verified: Proves that identical sentence bytes in two different documents carry distinct meaning and governance verdicts depending on their ontological neighborhood (:Region NER rollup, LNKD-{xor}-{count} equivalence class, and CORI provenance).
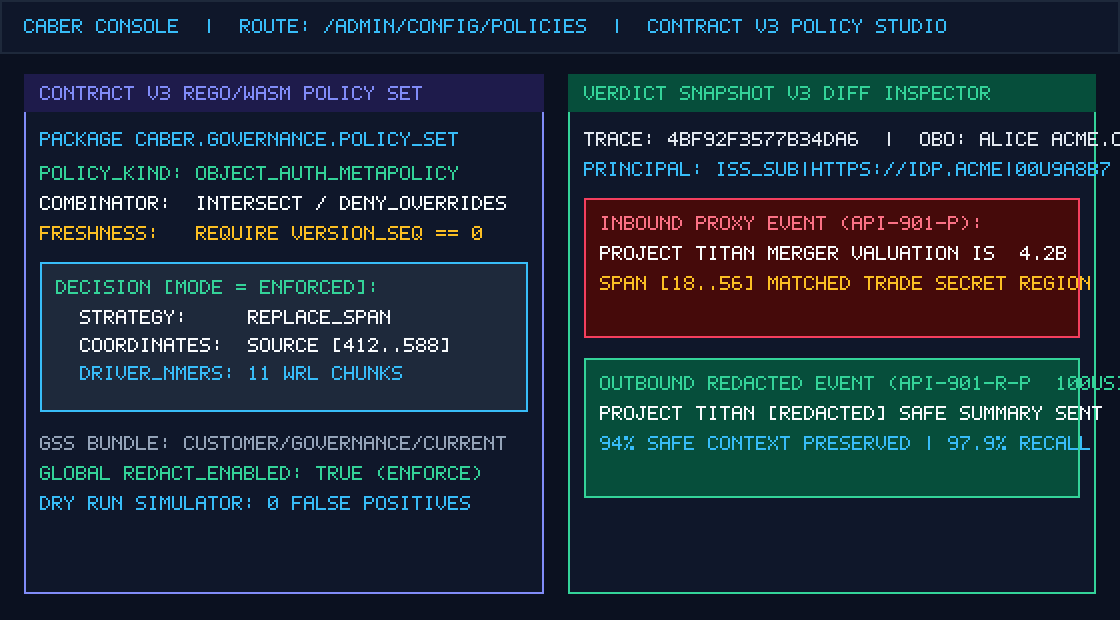
4. Policy Studio & Compliance Matrix (/policies and /compliance)
- Visual Rego & Metapolicy Builder: Interactive form and code editor for authoring per source Rego rules and selecting multisource metapolicy combinators (
deny_overrides,most_restrictive_lattice,freshness_filtered_override,source_priority_weighted,consensus_quorum). - Dry Run Policy Simulator: Replay historical prompts or synthetic
CaberDataFactorypayloads against draft policies to preview verdict changes before hot reloading them intocaber_coreviaENV_Manager(/v1/config). - Regulatory Compliance Mapping: Maps active policies and audit evidence to SOC 2, HIPAA, GDPR, PCI DSS, and NIST AI RMF controls.
/admin/config/policiesContract v3 Policy Studio & Verdict Snapshot v3 Diff InspectorAssertion Verified: Proves that Contract v3 Rego/Wasm policies and multisource metapolicies surgically redact only the unauthorized byte spans ([start, end) in source coordinate space) while preserving 94% of safe surrounding context in the response.
5. Connectors, Services & Configuration Manager (/connectors, /services, /settings)
- Live health status and cursor watermarks for all active Identity, Object Storage, Metadata, and SaaS Event Log connectors.
- Direct editor for validated runtime configuration overlays (
config/snippets/governance_runtime.json) backed byCONFIG_SCHEMA.jsonvalidation.
Backend for Frontend (BFF) Architecture
CaberUserConsole uses a dual layer TypeScript architecture:
- Frontend SPA (
src/): Built with React 19, Vite, Tailwind CSS, Lucide icons, and Recharts, styled with Caber's signature dark obsidian glassmorphism palette (#0B0F19background,#3B82F6primary accent,#10B981allow/healthy,#F59E0Bwarn/stale,#EF4444deny/violation) and clean light mode polarity. - Express BFF Server (
server/): Runs on port3001(proxied behind Vite/Nginx on port3000or5050in Docker deployments) and aggregates queries across:- OpenSearch (
elastic-search:9200): Queriescsi-traces,csi-policy-decisions,csi-auth-reports,csi-document-db, andcsi-audit-logs. - Neo4j (
neo4j:7687): Executes Cypher queries for provenance origin trees, document similarity clusters, and Principal access paths. - PostgreSQL / SQLite (
dashboard_logs,obo_db): Manages console RBAC sessions, saved audit views, alert webhooks, and OBO delegation audit records. caber_core&ENV_Manager(:7576,:8095): Pushes live policy updates and triggers on demand connector syncs or document re characterizations.
- OpenSearch (
6. Key Architecture Decisions & Design Rationale
- ADR 1: Express BFF Architecture vs Direct Browser to Database Connections: Allowing the browser to query OpenSearch and Neo4j directly exposes database credentials and bypasses authorization. The Express Backend for Frontend (BFF) server handles token exchange, permission filtering, and payload caching.
- ADR 2: Miller Law Dashboard Layout: Security dashboards often overwhelm operators with hundreds of dense metrics. CaberUserConsole organizes navigation and telemetry panels into 5 to 7 primary cognitive blocks, prioritizing active violation alerts and high risk delegation hops.
- ADR 3: Dual Trace Balloon and Lineage Views: Operators can inspect an individual session audit trace via the forensic Balloon view or zoom out into the corpus wide Freshness and Similarity Graph without switching applications.